Vietnamese firms face fines of up to 5% of revenue for personal data violations
Vietnamese businesses could face fines of up to 5% of their previous year's revenue for violations involving cross-border transfers of personal data, according to regulations that were informed at a seminar on data management risks and the legal requirements facing businesses held by the Vietnam Chamber of Commerce and Industry (VCCI) on November 17.
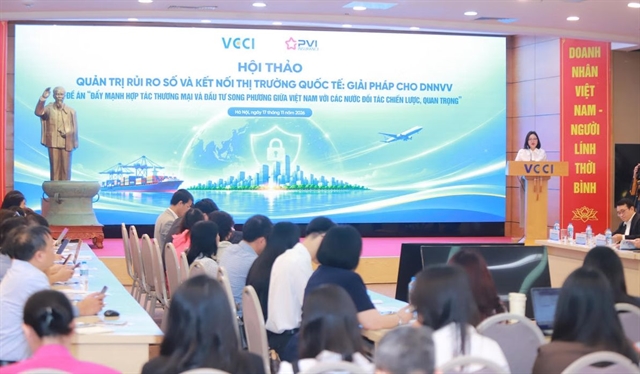
HÀ NỘI — Vietnamese businesses could face fines of up to 5 per cent of their previous year's revenue for violations involving cross-border transfers of personal data, a conference heard on November 17.
Speaking at a seminar on data management risks and the legal requirements facing businesses held by the Vietnam Chamber of Commerce and Industry (VCCI), Trần Thị Thanh Tâm, director of VCCI's Centre for Supporting Small- and Medium-sized Enterprises, said micro, small and medium-sized enterprises account for about 98 per cent of the more than one million businesses currently operating in Việt Nam.
These enterprises play an important role in job creation, local economic development and participation in supply chains. However, limited financial resources, staffing and technological expertise leave them particularly vulnerable to cybersecurity threats.
Citing figures from the Việt Nam National Cybersecurity Association, Tâm said Việt Nam recorded about 552,200 cyberattacks in 2025. Some 52.3 per cent of surveyed businesses reported having suffered losses, while around 25.5 million accounts were exposed.
Digital platforms allow smaller businesses to promote products, conduct transactions and serve customers across multiple markets at lower costs, Tâm said. However, business data, operational systems and commercial trust are also increasingly exposed to threats.
A fraudulent email impersonating a business partner, for example, could prompt an accountant to transfer money to the wrong bank account, while an outage affecting a sales system could disrupt transactions, delay deliveries and directly affect cash flow.
Ngô Việt Khôi, a security expert at Vietnam Data Security Joint Stock Company (VNDS), identified six common weaknesses in digital risk management among SMEs. They include a lack of dedicated personnel, insufficient budgets, over-reliance on individuals in operational procedures, the mixing of personal and business assets, dependence on third parties, and the absence of incident response plans.
Common practices such as sharing passwords, sending login credentials through Zalo, storing customer data in personal Gmail accounts or failing to revoke administrative access when employees leave can all result in data losses.
“SMEs are targeted because they are easy targets,” Khôi warned.
Data is not only stolen by hackers but can also leave a company through employees using poorly controlled methods, he said. The consequences may include lost customers, legal liabilities and reputational damage.
Legal compliance must be built into business operations
At the seminar, Major Nguyễn Tiến Đức, an officer at the General Advisory Division of the Ministry of Public Security's Department of Cybersecurity, said the Cybersecurity Law that takes effect on July 1, 2026, together with its implementing regulations, establishes requirements for information system protection, data storage, service provision and activities in cyberspace.
Under the law, organisations violating personal data protection requirements could face maximum fines of VNĐ3 billion (US$116,450). Violations involving cross-border transfers of personal data could attract fines of up to 5 per cent of the previous year's revenue, while the illegal purchase or sale of personal data could be penalised by fines of up to 10 times the proceeds obtained from the violations.
In addition to financial penalties, businesses could face suspension of operations for between one and 24 months, revocation of licences and orders to remedy the consequences of violations.
A key requirement is that businesses must determine the protection level of their information systems, ranging from Level 1 to Level 5, based on system functions, the data processed, users and system scale. Businesses are prohibited from splitting systems to obtain a lower protection classification.
SME information systems are generally classified as Level 2 or Level 3, he said. A system may be classified as Level 3 if it processes basic personal data belonging to at least 100,000 individuals, or sensitive personal data belonging to at least 10,000 individuals.
Lawyer Lưu Xuân Vinh of Asia Legal Law Firm said a small sized company does not exempt it from legal obligations.
Businesses need to identify the types of data they collect, where the data is stored, who has access to it, how long it is retained and the legal basis for processing it for each purpose.
Vinh also noted that cross-border transfers of personal data are not limited to sending data files overseas. Data stored on cloud platforms in Việt Nam but accessed and processed by foreign businesses may also fall within the scope of these regulations.
Digital risk management is not only meeting legal requirements but is also directly linked to businesses' ability to access international markets.
To turn connecting opportunities into substantive partnerships, businesses need to closely control the data they share, clarify its intended purpose and recipients, and define the responsibilities of each party in the event of an incident, the experts said.
Compliance with regulations and information protection can help minimise risks while building trust with international partners.
Tâm said legal compliance and digital risk management should be viewed as investments in business development rather than merely compliance costs.
For SMEs, measures ranging from data controls and access management to proactive incident response all contribute to protecting their reputation and competitiveness. —VNS