Early detection key to tackling growing business security risks
Việt Nam recorded more than 502 million leaked enterprise data records in the third quarter of 2025, highlighting the growing cybersecurity challenges facing businesses amid the increasing volume of sensitive corporate information.
HÀ NỘI — More than 502 million records of enterprise data were leaked in Việt Nam in the third quarter of 2025, highlighting growing cybersecurity risks for businesses as sensitive information becomes an increasingly valuable target.
The number of stolen personal accounts also reached 6.5 million during the period, up 64 per cent from the previous quarter, with the finance, banking, energy and critical infrastructure sectors among those most affected, according to Viettel Cyber Security (VCS).
While external cyberattacks remain a major concern, businesses also face risks from within their own organisations. Trusted employees with legitimate access to corporate information can, intentionally or unintentionally, expose sensitive data, facilitate fraud or misuse company resources.
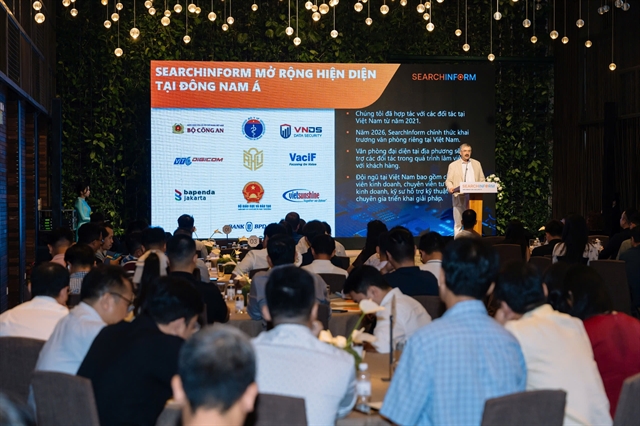
Hòang Tuấn Anh, Country Director of SearchInform Vietnam, said internal activities could pose significant risks when unusual behaviour is not detected at an early stage.
Employees may copy research and development documents to external devices, alter bank account details on invoices or share commercial information with competitors. Such activities can result in financial losses, customer outflows and damage to business operations.
A case involving a car dealership illustrates how internal risks can emerge from routine business activities. An investigation found that a sales manager had told a customer she was not entitled to a standard discount, before offering the same discount as a "special condition" in exchange for a personal cash payment to himself and his superior.
In another case, a manager was found to have passed potential customer leads to a competitor. The rival subsequently offered the same vehicles at lower prices, while part of the payment was requested in cash as compensation for the employee who provided the information.
One of the schemes could potentially have cost the dealership hundreds of thousands of US dollars a year, while the other posed a risk of losing customers. The company detected the activities by examining unusual employee behaviour and communications.
Similar risks can arise from relationships between employees and competitors. At a retail company, a sales manager planned to transfer information on potential customers to a competing business in exchange for money.
The activity was detected when the manager began copying the customer database to an external hard drive. The transfer was stopped and an internal investigation launched. The company estimated that potential losses could have reached millions of US dollars had the information been transferred.
Financial fraud is another area in which insider risks can be difficult to detect. A retail company received an email from a foreign supplier requesting payment for equipment to be made to a new bank account. The message initially appeared to be an external fraud attempt.
An investigation found, however, that an employee had received the supplier's genuine payment details and then used image-editing software to alter the bank account information on the invoice.
The invoice was worth US$370,000. Had the manipulation gone undetected, the company could have lost the money and faced a serious dispute with its supplier.
In another case, a dairy products company detected an employee attempting to send a confidential document containing budget, expense and revenue information to a colleague. Access to the document had been restricted to senior managers. The potential loss was estimated at about US$850,000.
Not all internal risks involve data theft or financial fraud. At another company, monitoring revealed that five of seven IT employees were spending between five and six hours of working time playing an online game. The company had not detected major attempts to leak data or sell customer information, but the findings highlighted problems with workplace discipline and productivity.
Hoàng Tuấn Anh said businesses should pay greater attention to internal risks alongside external cyber threats, particularly by controlling access to sensitive information and monitoring unusual activities.
Early identification of suspicious behaviour can help companies limit potential losses and strengthen the protection of corporate data, while also improving internal controls and workplace discipline. — VNS